The context
SASE has become the assumed direction of enterprise networking, with standalone SD-WAN increasingly treated as a phase rather than a destination. Adoption, however, is going badly for most organisations. Deployments stall — not on technology, but on funding redirected mid-programme and on internal disagreement about the business case. Data residency requirements in the Kingdom add a further constraint that generic cloud-delivered architectures do not address by default.
A consultancy of several hundred staff had a workforce that was almost never in the office. Client sites, home working and travel accounted for the large majority of working hours, while the security architecture still assumed a head office that most people rarely entered.
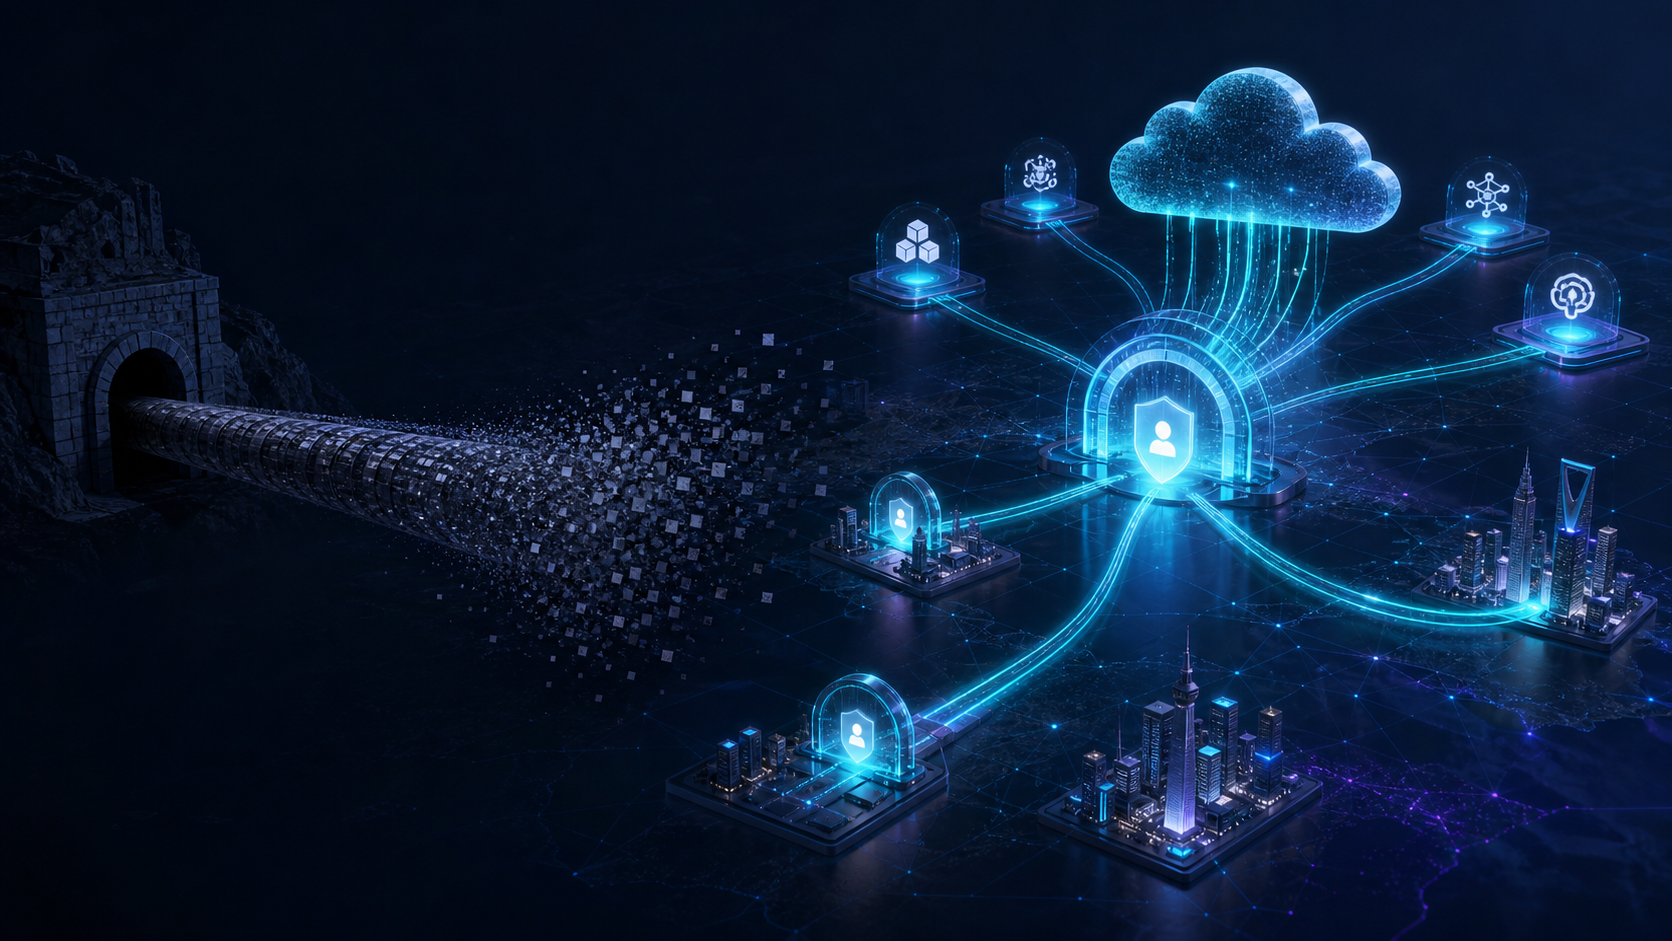
The practical consequence was a VPN carrying all remote traffic back to head office for inspection before going out again. Performance was poor enough that staff had found alternatives — cloud applications accessed directly outside the VPN, documents moved through personal accounts, and one department using a consumer file-sharing service nobody had approved. Every one of those decisions was rational for the person making it, and collectively they destroyed the security model.
The second problem was the access model itself. VPN grants network access, and network access is a poor proxy for application permission. A consultant needing one client-facing system received a path to everything.
The approach
ITBuilders started by mapping actual usage — which applications staff used, from where, on what devices — rather than the sanctioned list. Around a third of active applications were not on the sanctioned list, which is the normal ratio and the point of measuring.
Design moved inspection and policy enforcement away from the office and toward the user. Traffic is inspected where the user is, against a single policy set, whether they are at home, on a client site or in the office, and whether the destination is a cloud application or an internal system. Data residency requirements were addressed in the architecture rather than accepted as a platform default, with inspection and logging kept within required boundaries.
Application access was rebuilt on a per-application model with continuous verification. Access is granted to a named application based on identity, device posture and context, and re-evaluated during the session rather than at connection. A device falling out of compliance mid-session loses access without waiting for a reconnection.
Sanctioned cloud applications were brought under policy with visibility of data movement between them. Unsanctioned services were handled by providing a supported equivalent first and restricting afterwards, in that order. Restriction without a replacement produces a new workaround within weeks.
Delivery was sequenced deliberately, department by department, with the legacy VPN available in parallel until each group was stable. This matters more than the architecture. Programmes of this type fail when they require a single large budget decision and a simultaneous cutover; phased delivery produces visible results early enough to hold funding and internal support through the full programme.
ITBuilders holds Fortinet Engage Partner Specializations in both SASE and SD-WAN — relevant because the transition is rarely a single step. Most organisations arrive through their branch network, and the credential covering where they start is as material as the one covering where they are going.
What changed
Remote performance improved because traffic stopped taking a detour through head office. Data movement into unmanaged services became visible and then rare. Access permissions now describe applications rather than networks, which is both more restrictive and considerably easier to explain to an auditor.
Continuity of operation
ITBuilders continues to operate the policy estate — onboarding new applications, maintaining access rules as roles change, and reviewing posture requirements. A policy set that is not maintained becomes a permissions sprawl within two years, which is the same problem the organisation started with in a different form.